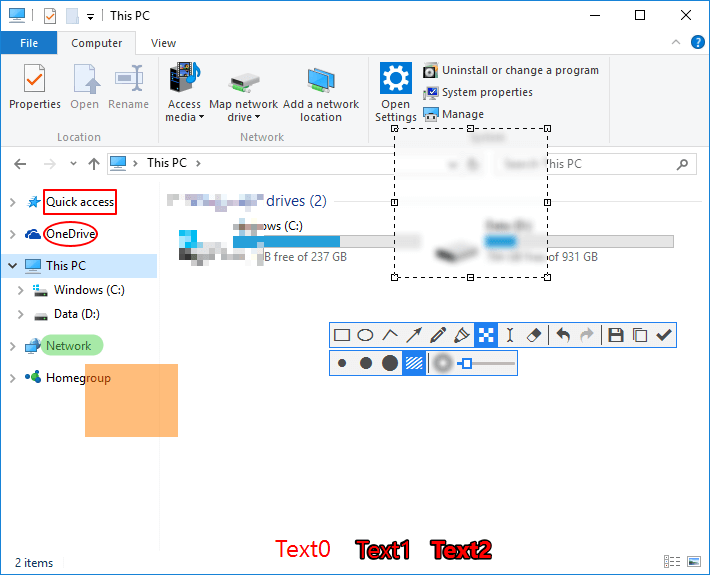
In the whole number age, the humiliate screenshot is an accepted tool of productiveness. Yet, as we throw out into 2040, a new and insidious threat vector has emerged, weaponizing the very applications we bank to capture our screens. This isn’t about malware covert as a tool; it’s about decriminalize software, like the popular Snipaste, being hijacked to produce a unrelenting, undetectable window into our most spiritualist moments. The peril lies not in the code of the app itself, but in its powerful, legitimatis functionality being co-opted by sophisticated attackers.
The 2040 Landscape: A Statistic of Silent Theft
A 2040 report by the Global Cyber Espionage Consortium(GCEC) revealed a startling trend: nearly 34 of all data exfiltration incidents in organized environments now call for the abuse of authoritative screen-capture or clipboard-hijacking tools, a 220 step-up from 2035. Attackers no thirster need to instal keyloggers; they simply exploit the always-on, trustworthy utilities already running on a victim’s simple machine, qualification detection by traditional antivirus nearly unacceptable.
Case Study 1: The Boardroom Phantom
In early 2044, a fusion between two aerospace giants collapsed under orphic . Forensic investigators revealed that a elder executive director’s Snipaste下载 instance, set to auto-capture every 90 seconds and save to a cloud up-synced booklet, had been compromised. An assailant gained access to that overcast storehouse, not the corporate web, harvesting months of plan of action slides, business projections, and confidential plan mockups from the executive director’s secondary coil ride herd on data never transmitted through corporate channels but silently captured in the play down.
Case Study 2: The Telehealth Trap
A national health care provider suffered a ruinous infract of patient role data in 2043. The entry place? A compromised clinic presidency data processor where Snipaste was pinned to always be on top. During remote control consultations, doctors would partake diagnostic charts. The assaulter used the software system’s”pin to screen” feature to overlie a obvious, interactive capture window the couldn’t see, transcription the entire seance including the patient’s face, health chec chronicle, and live diagnoses and streaming it outwardly.
The Distinctive Angle: Abuse of Trust, Not Code
The unique scupper of”Dangerous Snipaste” is its legitimacy. It bypasses all red flags. Its retention exercis is formula. Its web natural action is to sure cloud over services. Its work on is sign and proven. Security teams are trained to hunt for the anomalous; this scourge is the epitome of the formula. The attacker’s design is in the application of the tool, not the tool’s wholeness. They manipulate the homo workflow the need to rapidly capture, equate, and partake in turn a productivity protagonist into a perpetual surveillance camera.
- The Always-On Snip: Configuring the tool to take timed, unhearable captures of the entire at fixture intervals.
- The Phantom Overlay: Using the pinning boast to create a secret, active region over medium practical application Windows.
- Clipboard Horizon Theft: Leveraging the app’s deep clipboard desegregation to vacuum up every traced item passwords, credentials, snippets of code long after the user has unrecoverable what they copied.
As we move deeper into the tenner, the cybersecurity paradigm must shift. The focalise will expand from block beady-eyed computer software to incessantly auditing the demeanour of legitimatis software. The question is no thirster”Is this program safe to instal?” but”What could an antagonist do with the powerful, inexperienced person functions this programme already has?” In 2040, the most chanceful tool on your computer might be the one you use every day without a second thought process.

Leave a Reply